Meaning
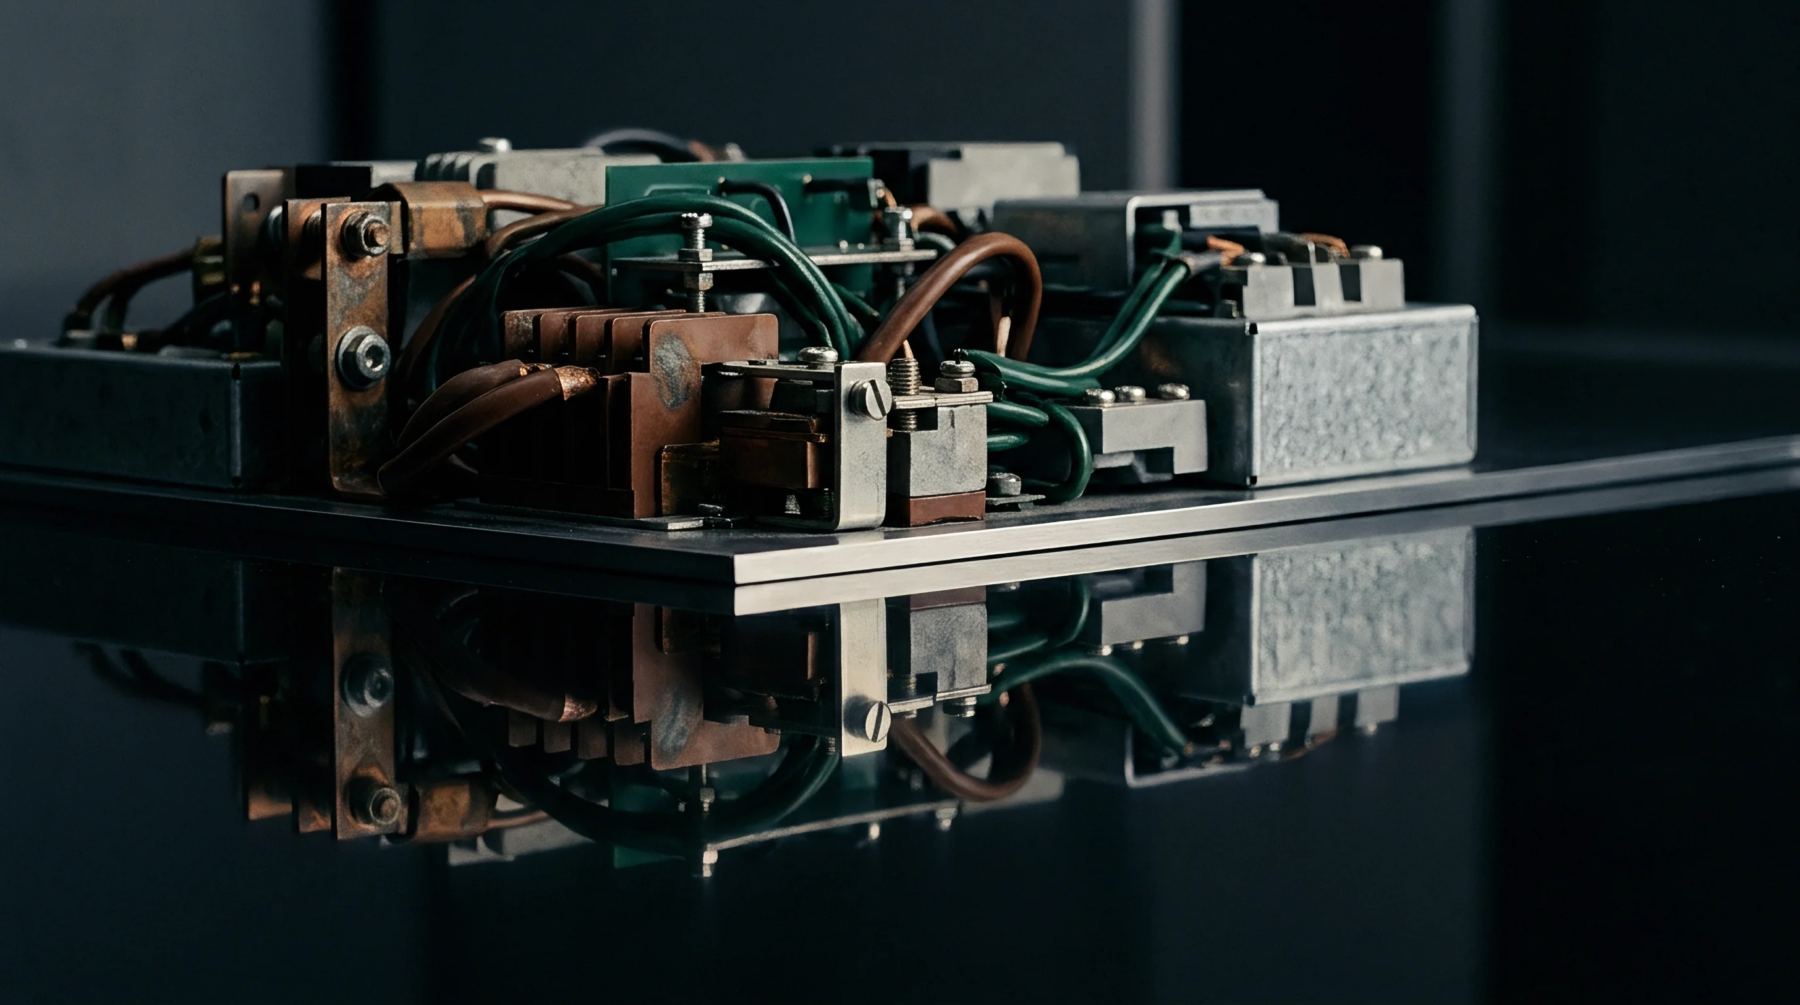
Specialized physical computing devices protect digital keys and execute high speed cryptographic operations within a tamper resistant enclosure to ensure identity integrity across a network. A hardware security module works by isolating secret identifiers from the general purpose software layers where they would be vulnerable to standard network based attacks. Verification occurs when an external procurement or bank interface requests a signature that only the local secure chip can provide without exposing the master key.
Boundaries restrict access to the device through rigid physical and logical barriers that limit the frequency and type of commands allowed. These modules safeguard the root of trust for large scale erp systems by managing the mathematical secrets that sign every official instruction or budget lock.
Internal Protections
Internal logic zeroizes the memory whenever sensors detect a physical breach attempt or an unauthorized case opening event on the hardware rack. Running transactions through a hardware security module ensures that identity theft remains technically impossible even if the host computer is fully compromised by external malware. Latency inside the unit remains extremely low to allow thousands of signings every hour for busy supply chain verification events.
Security audits verify that the key lifecycle happens entirely inside the device from generation through storage to final decommissioning without ever hitting system RAM. Diagnostic logs show how many active secrets are held within the partition and whether the available crypto processing capacity is reaching its limit. System health depends on reliable cooling and power since these devices perform continuous high density mathematical calculations that generate heat over time.
Readiness Evaluation
Scaling a prototype security system to a full production environment requires transitioning from software emulated keys to a genuine hardware security module array. Capacity tests identify how many parallel encryption streams the device handles before queue delays start to impact user experience during login or checkout. Capability assessments check if the hardware supports modern algorithms needed for long term data integrity in highly regulated procurement sectors.
Forecasted needs for key rotation help managers decide when to buy additional units to support the next generation of logistics growth. Calling a security configuration ready for production without a validated hardware unit creates a significant risk for identity spoofing and logical session hijacking. Successful implementation allows for high throughput without sacrificing the core confidentiality of the administrative identifiers used daily.
Enterprise Integration
Secure ledger environments integrate these devices into the signature path to ensure that every commitment is backed by an authenticated hardware event. Using a hardware security module creates a clear evidence trail that stands up in forensic reviews when officials need to verify the origin of high value contracts. Maintaining the device registry allows teams to verify that only authorized units are contributing signatures to the organizational record.
Forensic analysts look at the hardware interaction logs to confirm that all signed instructions followed the strict identity logic programmed into the chip. Preserving this hardware root of trust ensures the overall safety of the procurement environment from the foundational level up to the application surface.